Differences between mmWave and cameras in elder care scenarios
Compare information richness, privacy, installation, and verification methods
Conclusion: Select technology based on space, task, and user consent rather than pursuing a single solution for all rooms
Define the decision before discussing the solution
Non-visual sensing reduces identifiable imagery but still produces data about activity, dwell time, sleep and routine. Evaluation must cover physical coverage, signal quality, model version, environmental change, governance and human review.
Cameras facilitate human understanding of scenes but carry higher privacy pressures; mmWave does not generate identifiable video yet requires more scenario training and boundary definitions
“Compare information richness, privacy, installation, and verification methods” must be decomposed into population, life task, operating condition and observable result. “Clarify events requiring identification” fixes the problem and inputs, “Evaluate privacy sensitivity” tests entry into real workflow, and “Design verification methods” tests whether the conclusion survives contextual change; for “Compare information richness, privacy, installation, and verification methods”, without all three, technical capability, service accountability and partnership scope cannot be compared.
Three actions form one operating chain
Clarify events requiring identification
Validate “Clarify events requiring identification” through a bounded change: record room geometry, materials, device height and angle, occlusion, furniture, doors, pets, multiple people and connectivity so every result maps to an installation version. An improved average is insufficient without exceptions, non-completion and manual recovery, and the next step, “Evaluate privacy sensitivity”, retains the same population and definitions.
Evaluate privacy sensitivity
Acceptance of “Evaluate privacy sensitivity” requires function, comprehension, completed action and recovery. The operating method is to separate raw signal, feature, model inference, threshold, human label and final action rather than presenting inference as fact, then compare “User acceptance” at baseline, after change and during system unavailability.
Design verification methods
For “Design verification methods”, recalibrate and rerun representative scenarios after furniture, season, carer presence, firmware or model changes. The record also names the trigger, operator, input, completion evidence and exception takeover, then uses “Verification cost” to check whether burden merely moved to the older person, family or frontline staff.
These actions are not parallel recommendations. “Clarify events requiring identification” tests the problem definition, “Evaluate privacy sensitivity” tests entry into real work, and “Design verification methods” tests whether the result can be reviewed and sustained; removing “Design verification methods” makes this article confuse contextual evidence with general effectiveness.
Return the argument to one real use episode
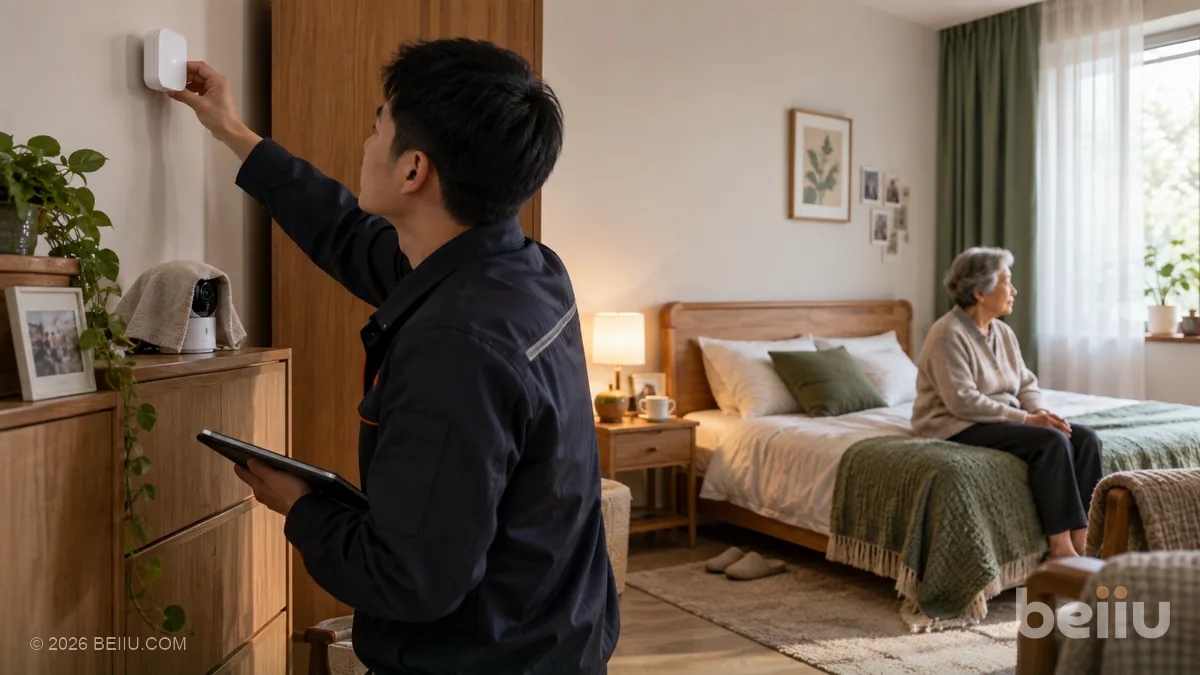
The same radar faces very different signal conditions in an open bedroom, a compact bathroom and a shared room. Furniture movement, pets, carers, doors and network instability can change outcomes, making installation and calibration part of the product rather than an after-sales detail.
Non-visual is not privacy-free. Define the minimum event before a pilot and avoid collecting unrelated routine. Installation drawing, calibration record, model version and permission list belong in acceptance evidence.
This article uses “Clarify events requiring identification” as the minimum task and “Covered tasks” across routine, exception, refusal and unavailable cases. In evaluating “Compare information richness, privacy, installation, and verification methods”, requirements, product, connectivity, interaction, response and ownership failures remain separate rather than hidden in an average.
“Select technology based on space, task, and user consent rather than pursuing a single solution for all rooms” supports scaling only when it continues through routine use and exception cases.
Every metric needs a denominator and context
- Covered tasks
For “Covered tasks”, report denominators, false alarms, misses and indeterminate output by room, event class, single or multiple people, occlusion and version. Retain the population, baseline, period, version and exception handling so the measure tests whether “Clarify events requiring identification” improved a real task rather than becoming a context-free promotional number.
- User acceptance
For “User acceptance”, separate device availability, data arrival, model availability and notification delivery because failure at any layer affects service. Retain the population, baseline, period, version and exception handling so the measure tests whether “Evaluate privacy sensitivity” improved a real task rather than becoming a context-free promotional number.
- Verification cost
For “Verification cost”, review recurring errors as cohorts and record whether a correction creates a new class of miss. Retain the population, baseline, period, version and exception handling so the measure tests whether “Design verification methods” improved a real task rather than becoming a context-free promotional number.
For “Covered tasks, User acceptance, Verification cost” describe different layers of demand, process and outcome and cannot collapse into one score. Safety analysis around “Covered tasks” includes misses, false alarms, unavailability and manual recovery; service analysis around “User acceptance” includes waiting, non-completion and recipient experience.
Plausible ideas can still produce the wrong system
- 01
equating non-visual with privacy-free
- 02
using laboratory motion sets as proxies for homes
- 03
assigning a multi-person event to the wrong individual
- 04
deploying model updates without revalidation
Stop deployment when the target room cannot be covered reliably, identity errors in multi-person scenes remain unexplained, performance drifts after updates, or the goal requires unnecessary collection.
For “Evaluate privacy sensitivity”, pause, human takeover, retest, exit and data deletion belong inside the product definition rather than a note written after failure.
The same system gives different roles different duties
- 01
users know what is collected and retained
- 02
installers record room and version conditions
- 03
model teams analyse misses and false alarms by scenario rather than one score
For “Compare information richness, privacy, installation, and verification methods”, “the family will monitor it” is not an operating model. Around “Evaluate privacy sensitivity”, name who receives information, confirms anomalies, handles emergencies, maintains equipment and changes rules; “User acceptance” without an owner or response time is not a service.
Use bounded validation instead of a large one-off rollout
For “Compare information richness, privacy, installation, and verification methods”, define the population and task, capture a baseline, agree data and consent boundaries, introduce a bounded change, record routine and failure cases, and use “Covered tasks, User acceptance, Verification cost” to continue, modify or stop. Every “Design verification methods” step retains its version and owner.
Before scaling “Design verification methods”, test whether value came from the intervention rather than extra labour, whether outcomes repeat across households or shifts, and whether maintenance, training and human takeover are budgeted; an unanswered “Verification cost” keeps “Select technology based on space, task, and user consent rather than pursuing a single solution for all rooms” narrow.
Professional judgement is explicit about uncertainty
BEIIU approaches “Compare information richness, privacy, installation, and verification methods” through a testable task: Select technology based on space, task, and user consent rather than pursuing a single solution for all rooms Around “Clarify events requiring identification”, the brand owns method and accountability rather than substituting its name for evidence, and keeps facts, findings, hypotheses and intentions separate.
The framework for “Compare information richness, privacy, installation, and verification methods” does not replace individual medical, care, legal or procurement assessment. Deployment of “Evaluate privacy sensitivity” still reviews functional ability, housing, local service capacity, regulation and personal choice.
What a reviewable project memorandum should contain
For “Compare information richness, privacy, installation, and verification methods”, begin with the original problem and current alternative rather than a predetermined product, then record who owns “Clarify events requiring identification, Evaluate privacy sensitivity, Design verification methods”, its conditions and when it should not occur so failure can be located in needs, design, installation, service or accountability.
The evidence chain for “Select technology based on space, task, and user consent rather than pursuing a single solution for all rooms” separates interview statements from interpretation, device observations from model inference, and pilot outcomes from future targets. For “Covered tasks, User acceptance, Verification cost”, retain denominator, period, attrition, version change and exception handling so incomplete cases remain visible.
A sensing project retains room geometry, placement, firmware and model versions, occlusion, pets, multiple-person entry and network state. Misses and false alarms return to a concrete scene and original timeline, with a new baseline after model updates or furniture moves.
A review of “Compare information richness, privacy, installation, and verification methods” places “Clarify events requiring identification” and “Covered tasks” in one evidence chain: the former states what changed and the latter how it was observed, and when they do not connect, improvement in “Covered tasks” does not establish improvement in “Clarify events requiring identification”.
For “Design verification methods”, define continuation, modification and stop conditions, including safety, privacy, acceptance or maintenance risks that trigger a manual path, so a later team can reconstruct the judgment behind “Select technology based on space, task, and user consent rather than pursuing a single solution for all rooms”.
Evidence base and use
The following sources establish policy, healthy-ageing, design, privacy or care boundaries for the topic; they do not validate a specific product by themselves.
- 01National People’s Congress: Personal Information Protection Law of the People’s Republic of China ↗
Supports analysis of purpose limitation, necessity, consent, sensitive information and individual rights.
- 02World Health Organization: Falls ↗
Supports treating falls as a multifactorial risk rather than a problem solved by one detection device.
- 03State Administration for Market Regulation: GB/T 45272-2025 Guidelines for Age-Friendly Home Product Design ↗
Supports a multidimensional view of age-friendly home products covering safety, usability, comfort, intelligence and health.
- 04Japan Ministry of Health, Labour and Welfare: Promotion of Care Technology ↗
Supports analysis of how Japan links care-technology adoption, workflow improvement, productivity and care quality.